India’s digital transformation has changed the way millions of people manage their money. From mobile banking and instant payments to online loans and digital identity verification, financial services have become faster and more accessible than ever. Yet this convenience rests on an often invisible foundation: the collection, storage and processing of personal information.
When that information is exposed, the consequences can extend far beyond the immediate incident.
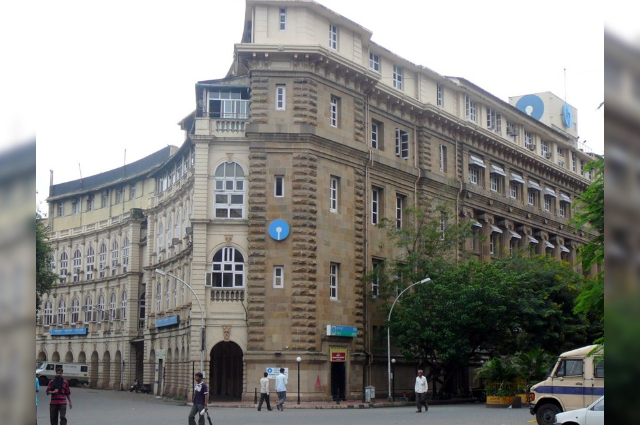
In October 2026, the State Bank of India (SBI) disclosed a suspected data exposure after alerts from its threat intelligence service provider, the Defence Cyber Agency and the Indian Computer Emergency Response Team (CERT-In). According to the bank’s disclosure reported by Hindustan Times and Mint, a preliminary examination of approximately 375,000 records identified 3,897 customer records containing personally identifiable information. The reported information included names, mobile numbers, dates of birth, email addresses, residential addresses, branch details and customer identification information. Metadata associated with loan and lead records was also reportedly present.
SBI activated its incident-response procedures and engaged an independent cybersecurity agency empanelled by CERT-In to investigate the authenticity, origin and extent of the suspected exposure. The bank stated that the incident had no material impact on its core operations, financial performance or business continuity. On October 23, it also said that it had individually notified the customers whose records had been identified and reiterated that their account balances and funds remained safe.
These assurances address an immediate concern, but they do not settle every question raised by the incident. The precise route through which the information became exposed, the full scope of the incident and the safeguards that may require strengthening are matters for investigation.
The central issue is therefore not simply whether money was stolen. It is whether personal information entrusted to a financial institution was adequately protected, how the exposure occurred and what accountability should follow.
When Personal Information Becomes a Security Risk
Banking security is often understood in financial terms. Customers worry about unauthorised withdrawals, fraudulent transfers and the loss of savings. These are serious risks, but they represent only one dimension of digital security.
Personal information can itself become a powerful instrument for fraud.
A criminal who possesses a person's name, mobile number, date of birth, address and banking-related identifiers may be better equipped to construct a convincing impersonation attempt. A fraudulent caller might claim to be contacting a customer about a loan application, an account verification issue or a suspicious transaction. Familiar details can make the caller appear credible, even when the person has no legitimate connection with the bank.
This technique is commonly associated with social engineering: manipulating people into disclosing information, authorising transactions or taking actions that compromise their security.
The danger is not that every exposed record will inevitably result in fraud. Rather, the combination of personal details can make targeted deception easier and more persuasive. Information that appears harmless in isolation may become more sensitive when combined with other records available online or obtained from unrelated incidents.
The distinction matters. An exposed database does not automatically mean that every affected customer will suffer financial loss, but neither does the absence of immediate loss establish that the exposure is harmless.
Personal data can create risks that persist after an incident has been contained. Once information has circulated beyond the control of the organisation that collected it, recalling every copy may be impossible.
The Difference Between Financial Security and Data Security
SBI’s assurance that customer funds and account balances remained safe was important. Customers needed to know whether their savings and banking services had been directly affected.
However, protecting money and protecting information are related but distinct responsibilities.
A bank may maintain the integrity of its core banking systems while customer information is exposed through another part of its technology environment, a connected service or an external party. These are possibilities investigators may examine; they should not be treated as established explanations for the SBI incident.
This distinction also explains why an organisation's statement that its operations remain unaffected does not, by itself, answer every privacy concern.
Operational continuity asks whether essential services continue to function. Data protection asks whether personal information has been accessed, disclosed or handled inappropriately, what harm may follow and how affected individuals will be protected.
Both matter to public trust.
A financial institution's responsibility should therefore extend beyond preventing unauthorised transactions. It must also safeguard the information customers provide, limit access to those who need it, monitor for suspicious activity and respond appropriately when an exposure is detected.
Accountability Begins Where Reassurance Ends
A public statement following a cyber incident is necessary, but it is only the beginning of an accountability process.
Customers deserve clear information about what is known, what remains uncertain and what the institution is doing to establish the facts. They also need practical guidance on recognising suspicious communications and obtaining assistance if they believe they have been targeted.
The SBI investigation raises several legitimate questions. What was the source of the exposed records? Were the records authentic and complete? How did the information become accessible? Did any third-party service or vendor have a role? What additional safeguards are needed to reduce the likelihood of recurrence?
These questions should be answered through the investigation rather than speculation.
It is equally important to distinguish between a question that remains unanswered and evidence that an institution has failed to act. A suspected exposure does not, on its own, establish negligence, deliberate concealment or a particular technical failure. Such conclusions require supporting evidence.
Nevertheless, uncertainty should not become an excuse for indefinite silence. Once findings can responsibly be disclosed, meaningful accountability requires more than a statement that an investigation has been completed. It requires an explanation of the incident's scope, appropriate corrective measures and clear communication with affected customers.
Where a failure to meet an applicable legal or regulatory obligation is established, the relevant authorities should determine the appropriate consequences.
The aim should not be to assign blame before the facts are known. It should be to establish the facts, correct weaknesses and ensure that customers are not left to navigate the consequences alone.
India's Evolving Data Protection Framework
India has taken an important step towards a more comprehensive approach to personal data protection through the Digital Personal Data Protection Act, 2023, and the Digital Personal Data Protection Rules, 2025.
The framework establishes responsibilities for organisations processing digital personal data and provides for safeguards, individual rights and regulatory oversight. Among its important principles are the protection of personal data, responsible processing and accountability for compliance.
However, the timing of implementation matters.
The Act and Rules provide for phased commencement, so not every provision became enforceable immediately upon notification. As of November 2026, the commencement schedule must be checked before asserting that a particular obligation or remedy already applies to the SBI incident. The incident's date, the relevant provision and its effective date all matter.
This distinction is particularly important when discussing breach notification. The DPDP framework provides for notification of personal data breaches to the relevant authority and affected individuals, but the applicability of those requirements must be assessed against the operative commencement provisions.
The absence of an immediately applicable provision under one framework would not necessarily mean that an institution has no obligations. Other applicable laws, regulatory directions and contractual requirements may also be relevant.
For banks, the regulatory context includes the Reserve Bank of India's requirements concerning information security, technology risk and cybersecurity. CERT-In's directions also establish reporting requirements for specified cyber incidents, including data breaches and data leaks. Under the 2022 directions, reportable incidents must be reported within six hours of noticing them or being brought to their notice, with additional information supplied subsequently where necessary.
These requirements serve different purposes. Incident reporting supports national cybersecurity response, banking regulation addresses the resilience and security of financial institutions, and data protection rules address the handling of personal information and the rights of affected individuals.
A credible accountability framework needs these responsibilities to work together rather than treating them as interchangeable.
The Responsibilities of Financial Institutions
Preventing data exposure requires more than installing security software or conducting occasional technical assessments. It requires an organisation-wide approach to information security.
First, institutions should collect and retain only the information necessary for legitimate purposes. Data that is not needed should not remain accessible indefinitely merely because storage is inexpensive.
Second, access should be restricted according to job responsibilities. Strong authentication, appropriate permissions, monitoring and regular access reviews can reduce the opportunities for misuse.
Third, security assessments should cover third-party providers and connected systems. Where vendors process customer information or have access to internal systems, their security practices and contractual responsibilities are part of the institution's wider risk environment.
Fourth, organisations should maintain tested incident-response plans. These should establish how an exposure will be investigated, how affected systems will be secured, who will make decisions and how customers and authorities will be informed where required.
Finally, institutions should evaluate whether corrective measures actually work. A completed investigation is not the same as a resolved security weakness. Follow-up testing, independent assessment where appropriate and clear responsibility for remediation help turn lessons into lasting improvements.
These measures cannot guarantee that every incident will be prevented. Their purpose is to reduce the likelihood and consequences of exposure and to ensure that failures are detected and addressed promptly.
Customers Need Protection, Not Just Precautions
Customers also have a role in protecting themselves against fraud, particularly after information has potentially been exposed.
They should never share one-time passwords, PINs or banking passwords with callers claiming to represent a bank. Suspicious links and unexpected requests for verification should be treated cautiously. Customers should use official banking channels to verify communications and report suspected fraud promptly.
An important lesson is that familiarity does not establish authenticity. A caller who knows a customer's name, address or loan details may still be a fraudster.
Customers who receive a breach notification should follow the institution's verified guidance and remain alert to unusual communications. They should not assume that a message is genuine simply because it contains personal information.
However, these precautions must not be confused with the institution's responsibility to protect data in the first place.
Customers cannot control an organisation's internal access permissions, vendor arrangements, storage practices or security architecture. Asking individuals to remain vigilant is sensible, but it is not a substitute for institutional safeguards.
A fair response recognises both responsibilities: organisations must protect the information they hold, and customers need accessible support when that protection may have failed.
What Meaningful Accountability Should Look Like
The SBI incident offers an opportunity to consider what an effective response to a suspected data exposure should involve.
A responsible process should include:
- Clear notification: Inform affected individuals through verified channels when required, explaining what information may be involved and what steps they should take.
- A credible investigation: Establish the authenticity, source, scope and circumstances of the exposure without presenting unverified explanations as facts.
- Practical customer support: Provide a clear point of contact for questions, reports of suspicious activity and assistance related to the incident.
- Corrective action: Address the weaknesses identified by the investigation and assess whether additional safeguards are needed.
- Appropriate regulatory engagement: Meet applicable reporting and cooperation requirements and respond to findings from competent authorities.
- Meaningful follow-up: Communicate material findings and relevant improvements when they can responsibly be disclosed, while protecting information whose release could create further security risks.
These are not merely public-relations measures. They are ways to demonstrate that an organisation treats the protection of customer information as a continuing responsibility.
Accountability should also be proportionate to the evidence. An incident does not automatically prove negligence, and the number of exposed records alone does not establish the full severity of the risk. The sensitivity of the information, the circumstances of exposure, the effectiveness of the response and the consequences for affected people all matter.
Beyond One Bank, Towards a Culture of Privacy
The SBI incident should be understood within the broader challenge of securing India's expanding digital economy. Banks, payment providers, technology companies and public institutions increasingly handle information that can affect people's financial security, privacy and personal lives.
Digital growth creates enormous benefits, but public confidence depends on whether those benefits are supported by reliable safeguards.
A mature digital economy must measure success not only by transaction speed, service availability or the number of people brought online. It must also consider how responsibly personal information is collected, how effectively it is protected and what happens when protection fails.
The measure of a strong institution is not that it can promise that incidents will never occur. No complex digital system can offer that guarantee. Its strength lies in reducing risks, detecting failures, communicating honestly, supporting affected individuals and demonstrating that corrective action has been taken.
For SBI, the investigation and subsequent measures will be important in establishing what happened and what lessons should follow. For India's financial sector, the broader lesson is already clear: the integrity of digital banking depends on both the security of financial transactions and the responsible handling of personal information.
Money may remain untouched while privacy is compromised. Recognising that distinction is the first step towards a more complete understanding of digital security.
Ultimately, trust cannot rest on reassurance alone. It must be earned through demonstrable safeguards, transparent communication and accountability grounded in evidence.
References
- Sharma, Sejal. “SBI flags ‘loss of certain data’ as 3,897 customer records surface on dark web.” Hindustan Times, 21 October 2026. - https://www.hindustantimes.com
- HT News Desk. “SBI informs 3,897 customers of dark web data leak, says funds are safe.” Hindustan Times, 23 October 2026. - https://www.hindustantimes.com/
- Mahar, Samriddhi. “SBI data leak raises fraud risks as bank probes exposure of customer records.” Mint, 21 October 2026. - https://www.livemint.com
- Government of India, Ministry of Electronics and Information Technology. Digital Personal Data Protection Act, 2023. - https://www.meity.gov.in
- Press Information Bureau, Government of India. “Government notifies DPDP Rules to empower citizens and protect privacy.” 14 November 2025. - https://www.pib.gov.in
- Indian Computer Emergency Response Team (CERT-In). Frequently Asked Questions on the Directions relating to Information Security Practices, Procedure, Prevention, Response and Reporting of Cyber Incidents under Section 70B of the Information Technology Act, 2000. May 2022.https://www.cert-in.org.in
- Reserve Bank of India. Master Direction on Information Technology Governance, Risk, Controls and Assurance Practices. 2023. - https://www.rbi.org.in/